FAQS
It is a defined, managed environment where your employees process, store, and transmit Controlled Unclassified Information (CUI). KeyOwner operates the infrastructure, security, patching, and backups. Your team works in a hosted Windows desktop, so CUI stays inside the enclave instead of on laptops and local servers.
No. Your IT team or IT provider keeps managing your network, laptops and workstations, and everything outside the enclave. KeyOwner operates the CUI enclave itself and works with your team on shared items such as user accounts and multi-factor authentication. It takes the most demanding, audit-heavy piece off your IT team’s plate.
No service can make a contractor compliant on its own. The enclave is designed to support NIST SP 800-171 and CMMC requirements. KeyOwner operates the controls allocated to the enclave, and you remain responsible for your people, policies, CUI handling, System Security Plan, and government submissions. We document which requirements are ours, which are shared, and which stay with you.
From a familiar computer, through a secure Remote Desktop Gateway, using their own credentials and Duo multi-factor authentication. They land in a full Windows desktop inside the enclave with the applications they need, such as Microsoft Office and CAD tools.
Yes. Each customer gets dedicated virtual machines, a separate Active Directory forest, its own network segment, and tenant-specific encryption keys.
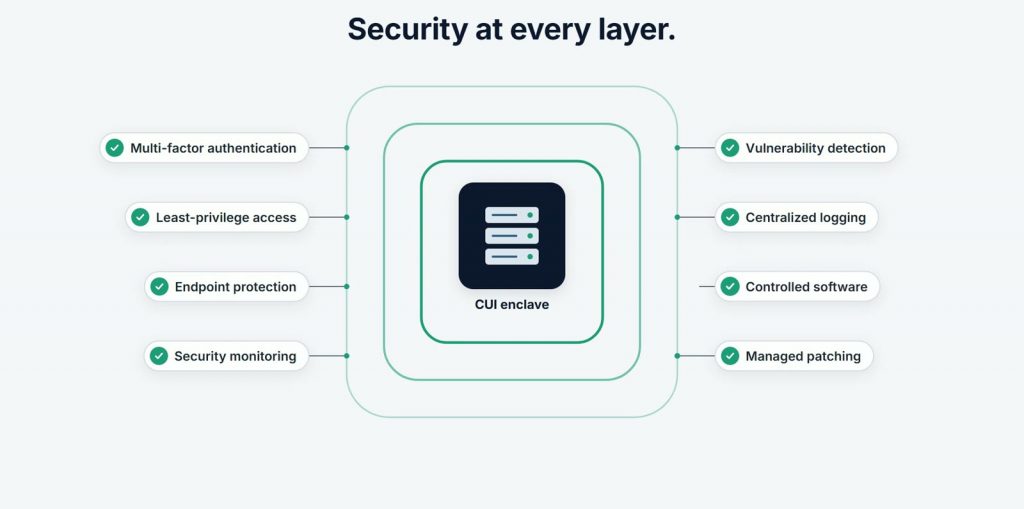
Protection is layered, from multi-factor authentication and least-privilege access to endpoint protection, logging, and managed patching. Connections are encrypted, stored CUI uses tenant-specific keys, and backups are encrypted before they leave primary storage. Encrypted daily backups are kept on-site and off-site.
KeyOwner collects audit logs, monitors security events, scans for vulnerabilities, and retains evidence for the controls it operates. You also receive documentation showing how responsibility for each requirement is divided between KeyOwner and your organization.
Small and midsized U.S. defense contractors and subcontractors that receive CUI and want a managed enclave for it, working alongside their existing IT team or IT provider.