Defense contracts come with security requirements and paperwork. KeyOwner runs your secure environment and prepares the SSP, responsibility matrix, and control evidence, lightening the load on your IT and compliance staff, so when your prime asks for documentation, you're ready to hand it over. Designed to support NIST SP 800-171 under DFARS 252.204-7012, with predictable monthly pricing scoped to your team.
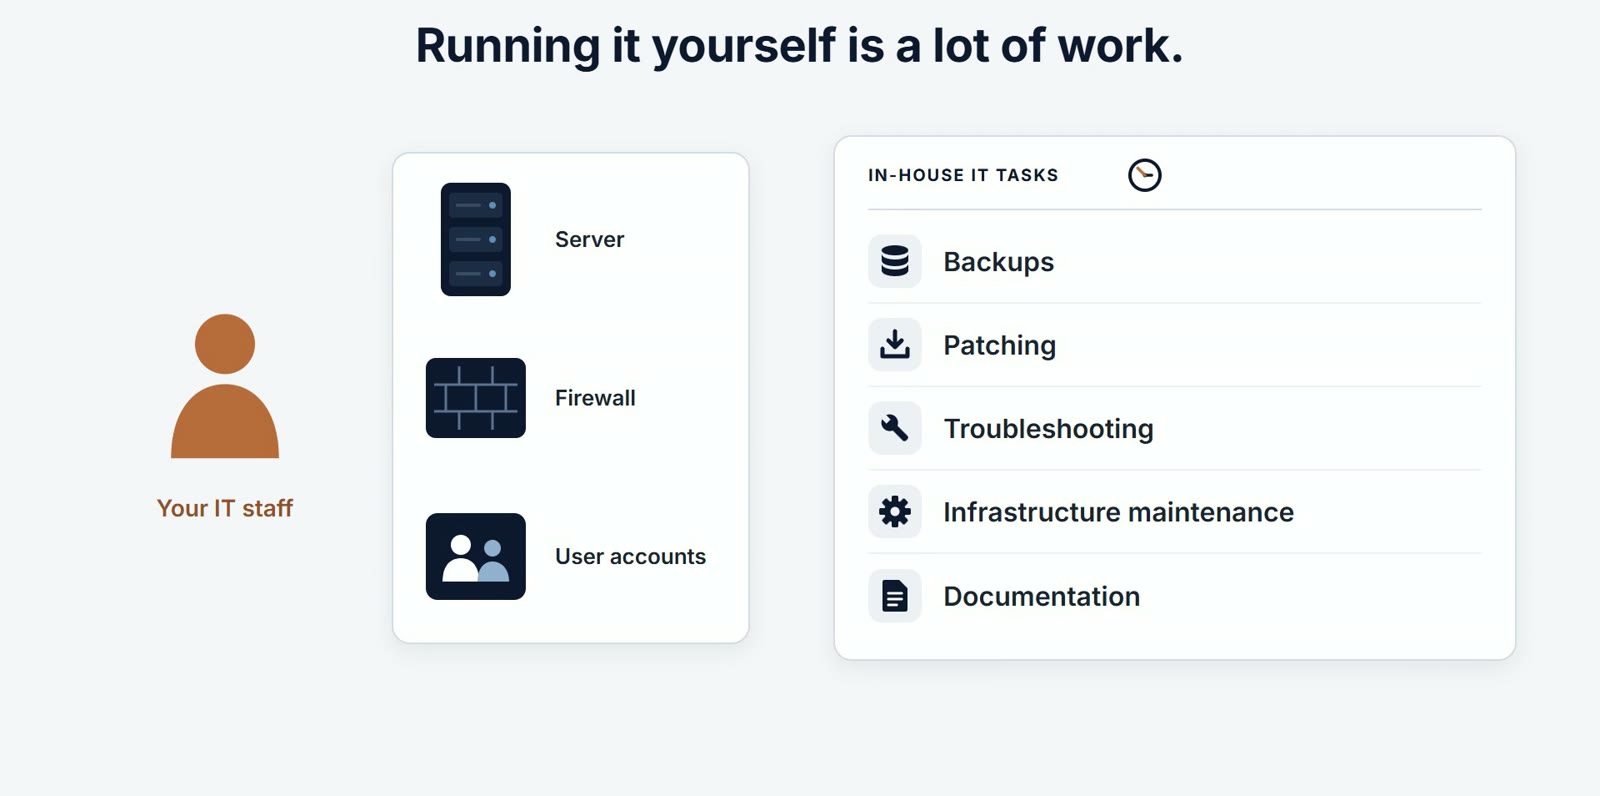
Handling CUI means backups, patching, troubleshooting, and infrastructure upkeep, all documented to an assessor’s standard, on top of everything your IT team already supports. If covered defense information is affected by an incident, DFARS requires reporting to the Department of Defense within 72 hours and preserving evidence for 90 days.
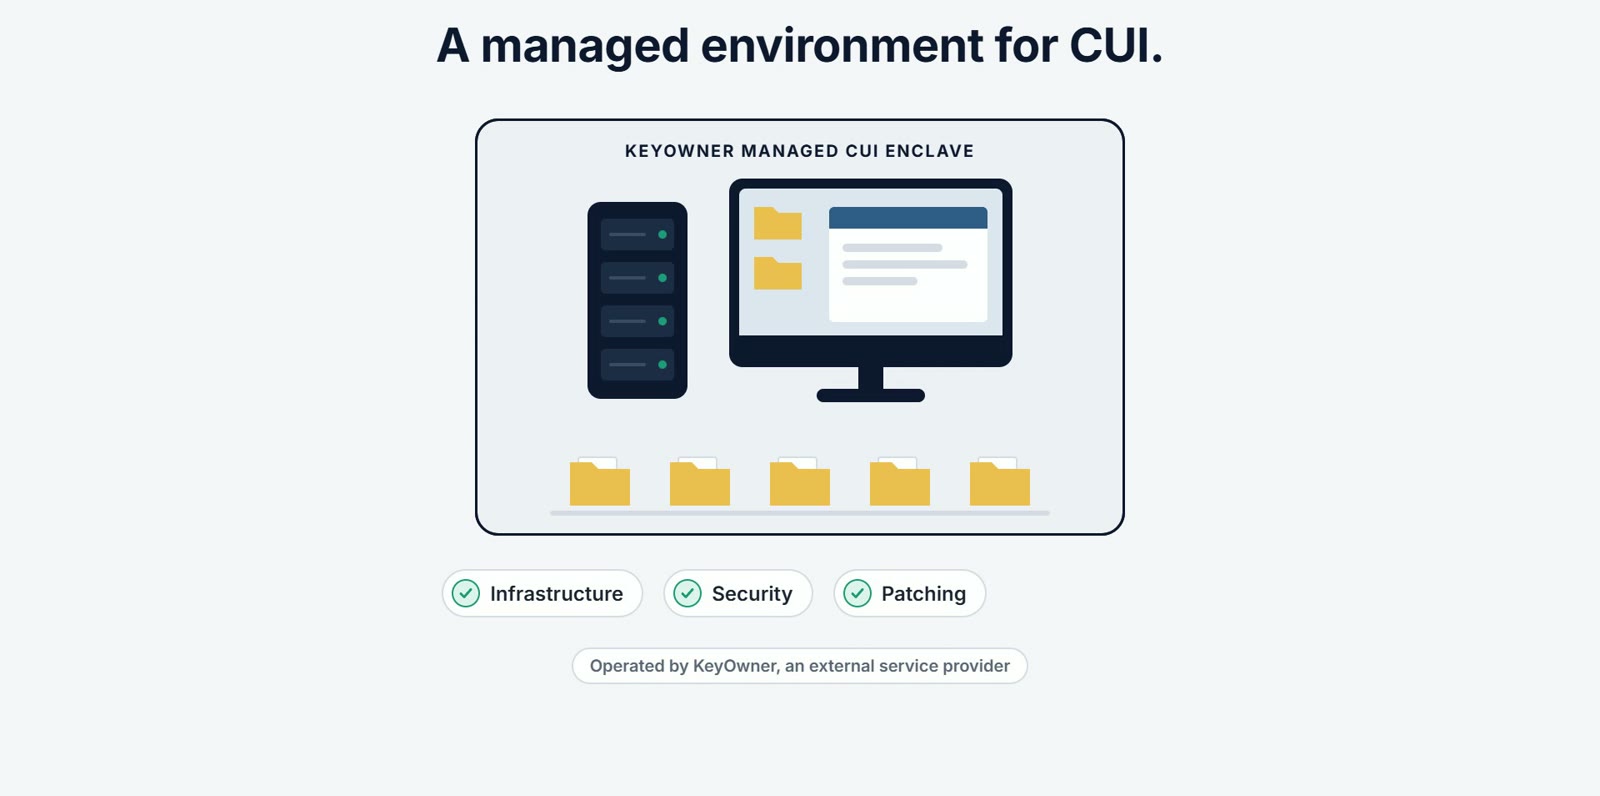
KeyOwner operates the enclave’s infrastructure, security, patching, and backups, while your IT team keeps running the rest of your environment. Employees connect through a secure Remote Desktop Gateway with their own credentials and Duo multi-factor authentication, to a full Windows desktop inside the enclave.
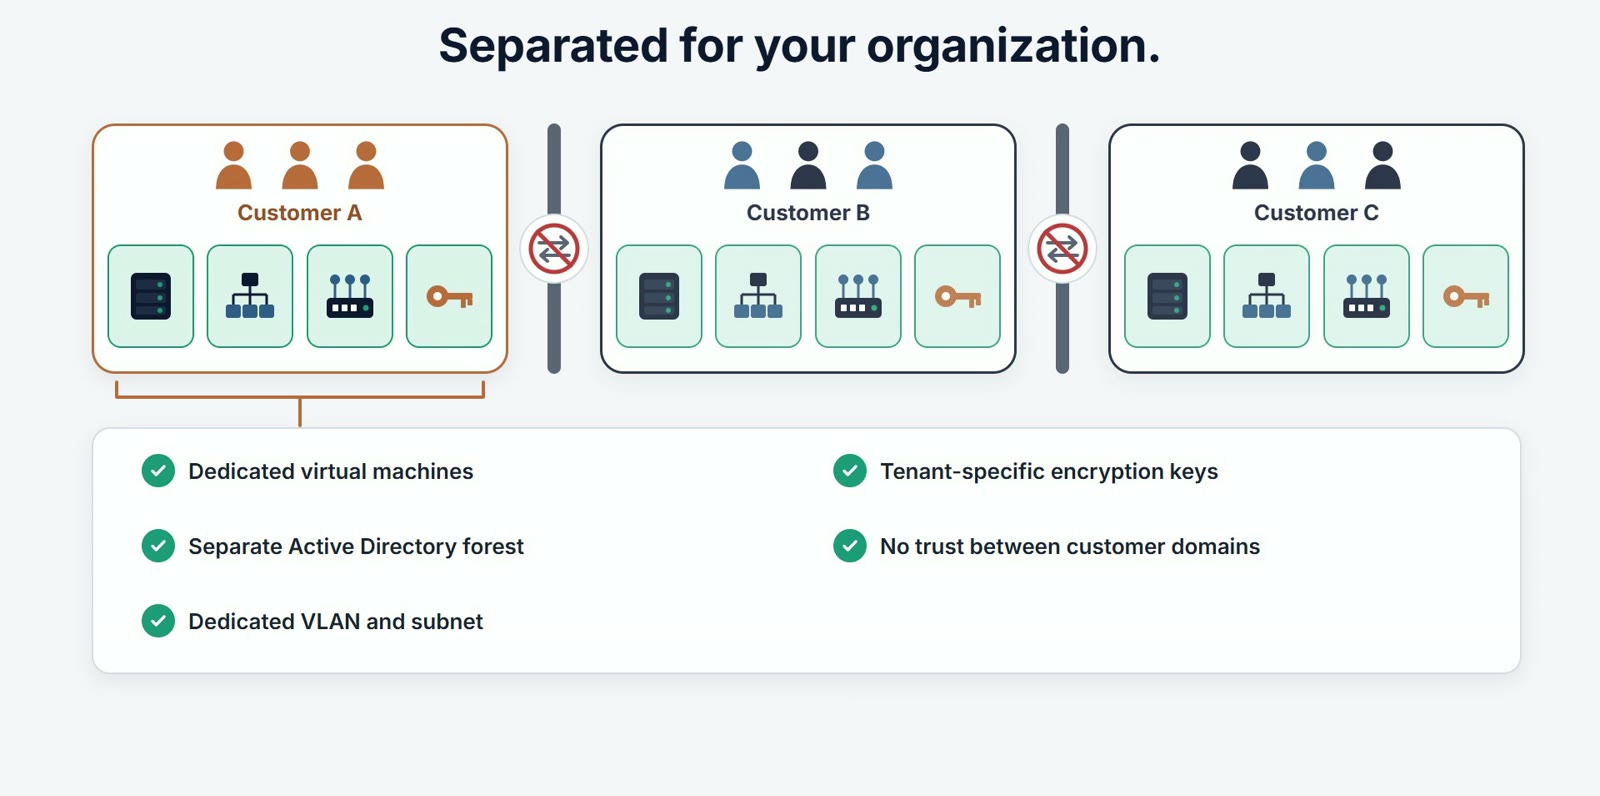
Each customer gets dedicated virtual machines, a separate Active Directory forest, its own network segment, and tenant-specific encryption keys. Connections are encrypted, stored CUI uses tenant-specific keys, and backups are encrypted before they leave primary storage.
Employees work with engineering files, Microsoft Office, and CAD tools through a hosted desktop. Applications and CUI stay inside the enclave.
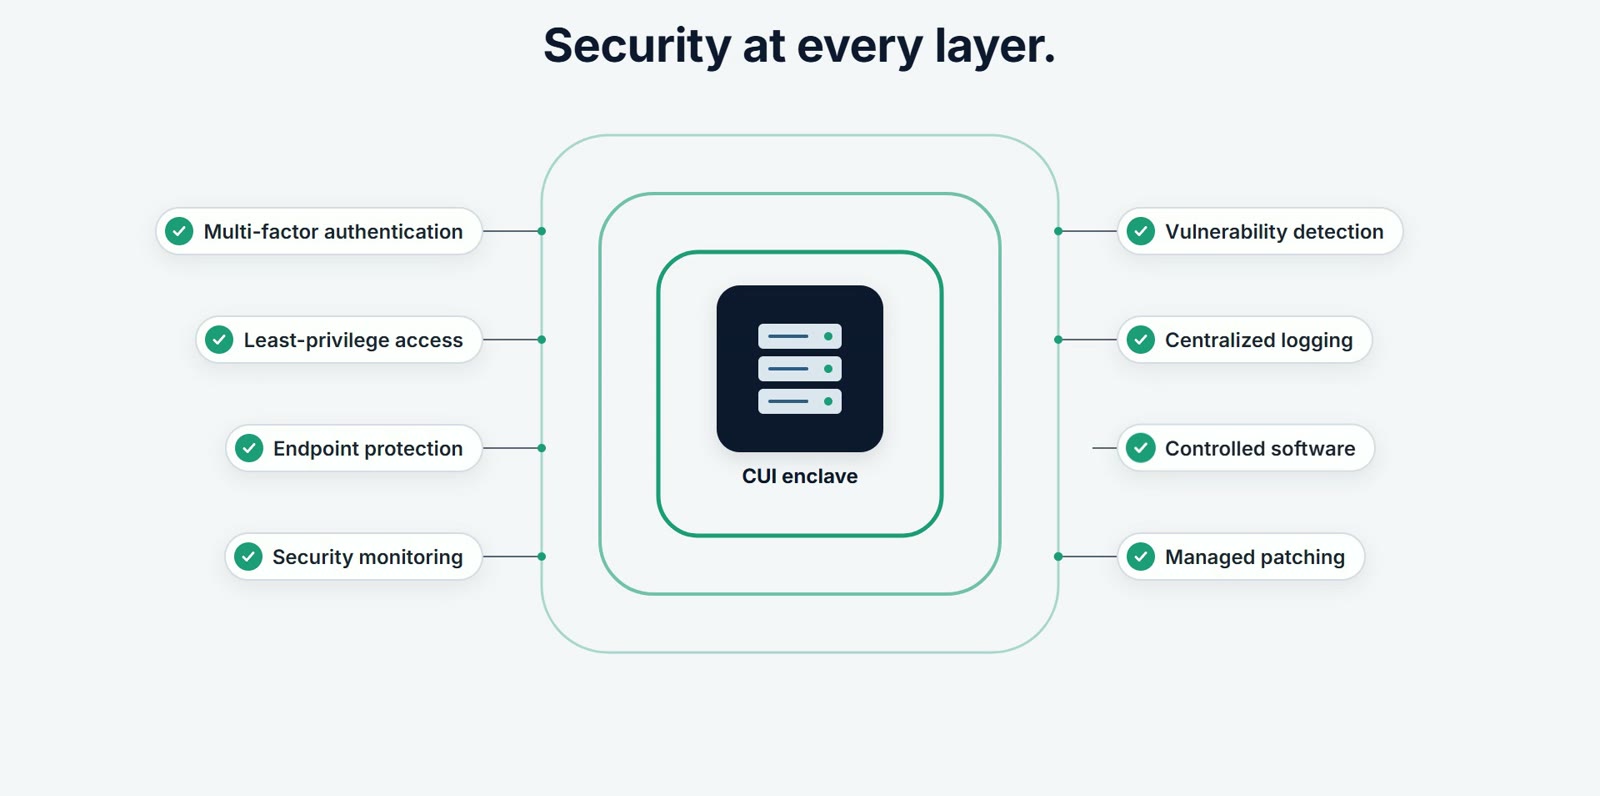
KeyOwner collects audit logs, monitors security events, scans for vulnerabilities, and retains evidence, with encrypted daily backups kept on-site and off-site.
The infrastructure, hosted security controls, patching, backups, monitoring, and technical evidence allocated to the enclave.
Your people, policies, CUI identification and handling, employee training, System Security Plan, and government submissions.
The enclave is designed to support NIST SP 800-171 and CMMC requirements. It does not make you compliant on its own, and we document how each requirement is divided.
Conversation: We meet with you and your IT team or IT provider to review which DFARS clauses are in your contracts and where controlled data lives today.
Onboarding: We set up your dedicated enclave and coordinate user accounts and multi-factor authentication with your IT team.
Migration: We work with your team to move CUI and engineering files into the enclave.
Operation: KeyOwner manages the enclave’s infrastructure, patching, backups, monitoring, and evidence for the controls it operates. Your IT team stays in charge of everything else.
It is a defined, managed environment where your employees process, store, and transmit Controlled Unclassified Information (CUI). KeyOwner operates the infrastructure, security, patching, and backups. Your team works in a hosted Windows desktop, so CUI stays inside the enclave instead of on laptops and local servers.
No. Your IT team or IT provider keeps managing your network, laptops and workstations, and everything outside the enclave. KeyOwner operates the CUI enclave itself and works with your team on shared items such as user accounts and multi-factor authentication. It takes the most demanding, audit-heavy piece off your IT team’s plate.
No service can make a contractor compliant on its own. The enclave is designed to support NIST SP 800-171 and CMMC requirements. KeyOwner operates the controls allocated to the enclave, and you remain responsible for your people, policies, CUI handling, System Security Plan, and government submissions. We document which requirements are ours, which are shared, and which stay with you.
From a familiar computer, through a secure Remote Desktop Gateway, using their own credentials and Duo multi-factor authentication. They land in a full Windows desktop inside the enclave with the applications they need, such as Microsoft Office and CAD tools.
Yes. Each customer gets dedicated virtual machines, a separate Active Directory forest, its own network segment, and tenant-specific encryption keys.
Protection is layered, from multi-factor authentication and least-privilege access to endpoint protection, logging, and managed patching. Connections are encrypted, stored CUI uses tenant-specific keys, and backups are encrypted before they leave primary storage. Encrypted daily backups are kept on-site and off-site.
KeyOwner collects audit logs, monitors security events, scans for vulnerabilities, and retains evidence for the controls it operates. You also receive documentation showing how responsibility for each requirement is divided between KeyOwner and your organization.
Small and midsized U.S. defense contractors and subcontractors that receive CUI and want a managed enclave for it, working alongside their existing IT team or IT provider.